How do you handle the Cyber Resilience Act next to a GRC platform?
Keep the GRC platform for organisation controls such as ISO 27001 and NIS2, and add a product record for the Cyber Resilience Act. Article 14 reporting for each product has applied since 11 September 2026.
Key takeaways
- A GRC platform tracks controls for the organisation, and the Cyber Resilience Act sets duties for each product with digital elements that a manufacturer places on the EU market.
- Article 14 reporting of actively exploited vulnerabilities and severe incidents has applied since 11 September 2026, and the other CRA obligations apply from 11 December 2027.
- CVD Portal Reporting adds a public disclosure portal, the Article 14 stage packages and CSAF advisories for €99 per month, billed annually.
- The CVD Portal evidence pack turns 12 months of vulnerability handling into PDF and CSV files for ISO/IEC 27001 control 8.8 and NIS2 Article 21(2)(e).
- A person uploads the evidence pack to the control in the GRC platform, so no integration has to be set up.
Which CRA duties sit on each product?
The Cyber Resilience Act gives the manufacturer duties for each product with digital elements. A GRC platform records controls for the organisation, so these duties need a record of their own for each product.
Only Article 14 applies now. Every other duty in the table applies from 11 December 2027 (Article 71(2)).
| Duty | Basis | Applies from | In CVD Portal Reporting | File in the evidence pack |
|---|---|---|---|---|
| Notify each actively exploited vulnerability and each severe incident to the coordinating CSIRT and ENISA, in three stages | Article 14(1) to (4) | 11 September 2026 | A package for each stage with its deadline. A person at your company submits each stage on the ENISA Single Reporting Platform. | vulnerability-reports.csv |
| A single point of contact that users can find, also for reporting vulnerabilities | Article 13(17) | 11 December 2027 | A public disclosure portal on your own subdomain, and a security.txt file | 00-summary.pdf |
| Address and remediate vulnerabilities without delay | Annex I Part II, point (2) | 11 December 2027 | Triage, the remediation decision with its rationale, and fix verification for each report | vulnerability-reports.csv |
| Publicly disclose information about fixed vulnerabilities once a security update is available | Annex I Part II, point (4) | 11 December 2027 | Published advisories in CSAF 2.0 | advisories.csv |
| Put in place and enforce a policy on coordinated vulnerability disclosure | Annex I Part II, point (5) | 11 December 2027 | A disclosure policy published on the portal | disclosure-policy.md |
| Provide a contact address for the reporting of vulnerabilities | Annex I Part II, point (6) | 11 December 2027 | The portal address, also listed in security.txt | 00-summary.pdf |
How does the evidence pack reach the GRC platform?
A person downloads one ZIP file from the Analytics page and uploads it to the vulnerability management control. The pack covers the 12 months before the download.
- Handle each vulnerability report in CVD Portal, from receipt to fix verification.
- Open Analytics and download the evidence pack.
- Upload 00-summary.pdf to the control in the GRC platform, then attach the CSV files to the same control.
The pack goes to a third party, so it holds no report content, no reporter name or contact and no internal note. It records that each step happened and when. A control with no records in the period says so in its status.
The evidence pack documentation lists every file and how each figure is counted.
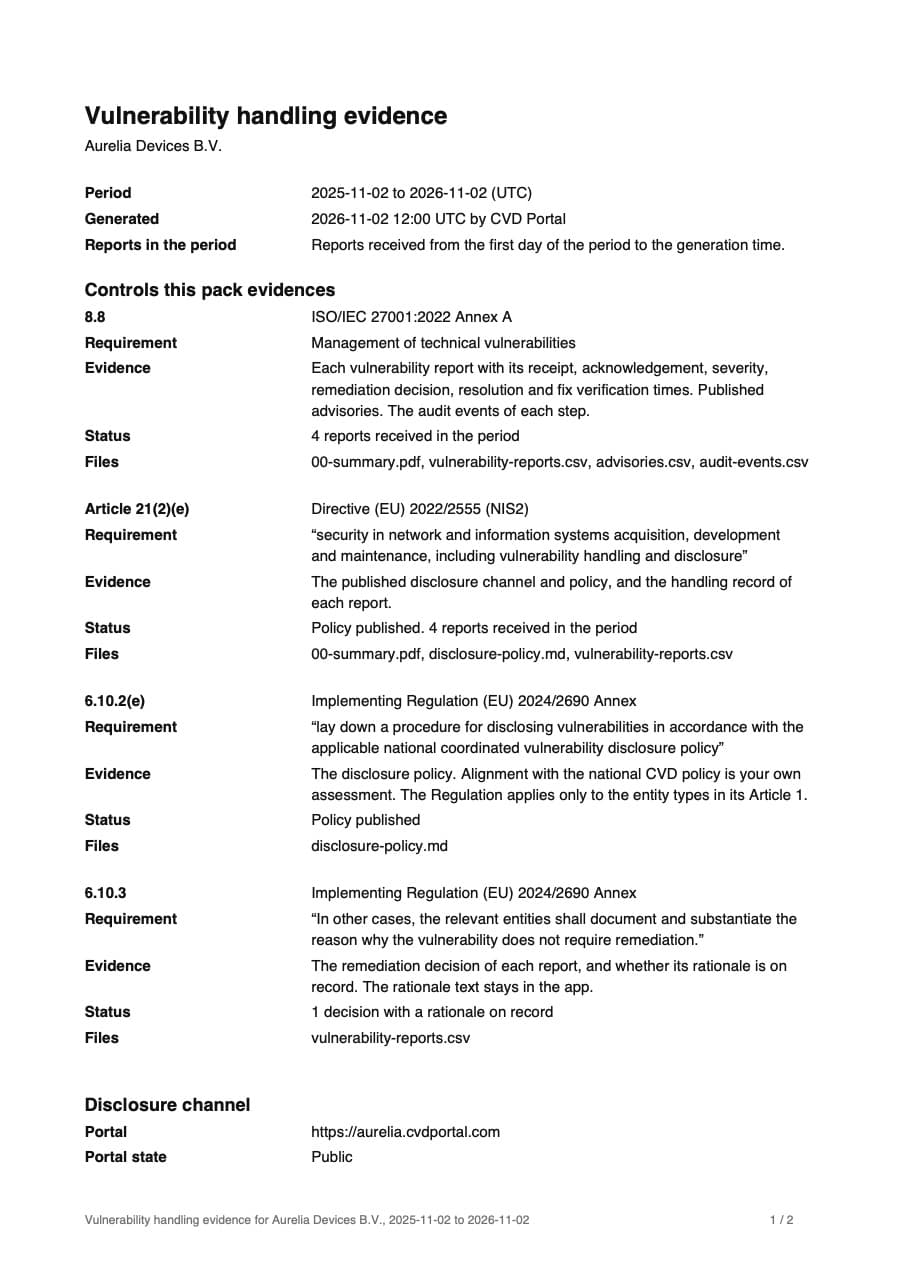
Which controls does the evidence pack support?
Four controls. Implementing Regulation (EU) 2024/2690 applies only to the entity types in its Article 1, for example cloud computing and managed service providers. NIS2 Annex II, point 5, lists manufacturers of computer, electronic and optical products, electrical equipment and machinery.
| Framework | Control | What the pack shows |
|---|---|---|
| ISO/IEC 27001:2022, Annex A | 8.8 Management of technical vulnerabilities | Each report with its receipt, acknowledgement, remediation decision, resolution and fix verification. The published advisories. The audit events of each step. |
| NIS2, Directive (EU) 2022/2555 | Article 21(2)(e), vulnerability handling and disclosure | The published disclosure channel and policy, and the handling record of each report. |
| Implementing Regulation (EU) 2024/2690 | Annex, point 6.10.2(e) | The disclosure policy. Whether it agrees with your national CVD policy is your own assessment. |
| Implementing Regulation (EU) 2024/2690 | Annex, point 6.10.3 | The remediation decision of each report and whether its rationale is on record. |
What does CVD Portal add next to the GRC platform?
The Reporting plan covers the duties that apply now, at €99 per month billed annually as €1,188 plus VAT.
- A disclosure portal on your own subdomain receives researcher reports, with a security.txt file.
- Each Article 14 stage has a prepared package and a deadline. An authorised person submits it on the ENISA Single Reporting Platform.
- Fixed vulnerabilities get a published advisory in CSAF 2.0.
- The evidence pack sends the handling record to the GRC control.
From 11 December 2027, the Compliance plan adds the classification, Annex I, the technical documentation and the EU declaration of conformity in the same product record. The pricing page compares the plans, and the Vanta and Drata comparisons go row by row.
Frequently asked questions
Does CVD Portal replace Vanta, Drata or Tidal Control?
No. Keep the GRC platform for ISO 27001, SOC 2 and NIS2. CVD Portal keeps the product record that the Cyber Resilience Act asks for, and the evidence pack sends the handling record back to the GRC control.
Does the evidence pack connect to the GRC platform by API?
No. A person downloads the ZIP file from the Analytics page and uploads the files to the vulnerability management control. The files are PDF, CSV and Markdown.
Which plan includes the evidence pack?
The Reporting plan, at €99 per month billed annually as €1,188 plus VAT. The Compliance and Enterprise plans include it too.
Does NIS2 compliance cover the Cyber Resilience Act?
The two laws apply separately. NIS2 sets duties for the entity and its network and information systems. The Cyber Resilience Act sets duties for each product with digital elements that a manufacturer places on the EU market. A manufacturer of electronic products can have both.
What applies from 11 December 2027?
All other CRA obligations, for example the Annex I essential requirements, the technical documentation and the EU declaration of conformity (Article 71(2)). The Compliance plan covers them in the same product record.
Sources
- Regulation (EU) 2024/2847, the Cyber Resilience Act, EUR-Lex CELEX:32024R2847. Articles 13, 14 and 71, and Annex I Part II.
- Directive (EU) 2022/2555, the NIS2 Directive, EUR-Lex CELEX:32022L2555. Article 21(2)(e) and Annex II.
- Commission Implementing Regulation (EU) 2024/2690, EUR-Lex CELEX:32024R2690. Article 1 and Annex points 6.10.2(e) and 6.10.3.
This page summarises the text of the three acts above. It is not legal advice. ISO/IEC 27001 is named by its control number and title only.
Published by Porta Regulus B.V., KvK 42062307. Read the editorial policy.
Last updated on 2026-11-02.
Add CRA reporting next to your GRC platform
Start a trial to publish your disclosure portal, prepare the Article 14 stages and download your first evidence pack.